
Latest Palo Alto Networks PCNSE Free Certification Exam Material with 375 Q&As
UPDATED PCNSE Exam Questions Certification Test Engine to PDF
The PCNSE exam is a comprehensive test that covers a wide range of topics including Palo Alto Networks technologies, advanced security features, network security concepts, and best practices. PCNSE exam is designed to validate the knowledge and skills of security engineers who have experience working with the Palo Alto Networks platform. Palo Alto Networks Certified Network Security Engineer Exam certification program is intended for professionals who want to demonstrate their expertise in network security and the latest technologies.
To prepare for the PCNSE exam, candidates can take advantage of a range of training resources provided by Palo Alto Networks, including online courses, instructor-led training, and self-study materials. The PCNSE exam is also available in multiple languages, making it accessible to a global audience.
NEW QUESTION # 63
Refer to the exhibit.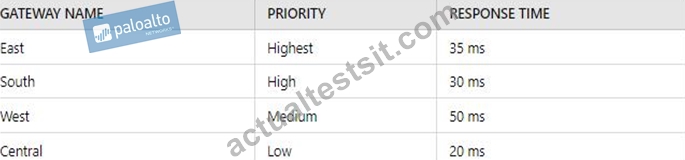
A security engineer has configured a GlobalProtect portal agent with four gateways Which GlobalProtect Gateway will users connect to based on the chart provided?
- A. West
- B. South
- C. Central
- D. East
Answer: D
Explanation:
Based on the provided table, the GlobalProtect portal agent configuration includes four gateways with varying priorities and response times. Users will connect to the gateway with the highest priority and, if multiple gateways share the same priority, the one with the lowest response time.
Answer Determination
Prioritize by Priority Level:
East: Highest
South: High
West: Medium
Central: Low
Evaluate Response Times Within Each Priority:
East (Highest): 35 ms
South (High): 30 ms
West (Medium): 50 ms
Central (Low): 20 ms
Given the highest priority is "East" with a response time of 35 ms, users will connect to the East gateway based on the highest priority.
NEW QUESTION # 64
What are the differences between using a service versus using an application for Security Policy match?
- A. Use of a "service" enables the firewall to take action after enough packets allow for App-ID identification
- B. Use of a "service" enables the firewall to take immediate action with the first observed packet based on port numbers Use ofan "application" allows the firewall to take action after enough packets allow for App-ID identification regardless of the portsbeing used.
- C. There are no differences between "service" or "application" Use of an "application" simplifies configuration by allowing use ofa friendly application name instead of port numbers.
- D. Use of a "service" enables the firewall to take immediate action with the first observed packet based on port numbers. Use ofan "application" allows the firewall to take immediate action it the port being used is a member of the application standardport list
Answer: B
NEW QUESTION # 65
If an administrator does not possess a website's certificate, which SSL decryption mode will allow the Palo Alto networks NGFW to inspect when users browse to HTTP(S) websites?
- A. SSL Forward Proxy
- B. SSL Outbound Inspection
- C. TLS Bidirectional proxy
- D. SSL Inbound Inspection
Answer: D
NEW QUESTION # 66
A firewall should be advertising the static route 10.2.0.0/24 Into OSPF. The configuration on the neighbor is correct, but the route is not in the neighbor's routing table.
Which two configurations should you check on the firewall? (Choose two.)
- A. Ensure that the OSPF neighbor state Is "2-Way."
- B. Within the redistribution profile ensure that Redist is selected.
- C. In the OSFP configuration, ensure that the correct redistribution profile is selected in the OSPF Export Rules section.
- D. In the redistribution profile check that the source type is set to "ospf."
Answer: B,C
NEW QUESTION # 67
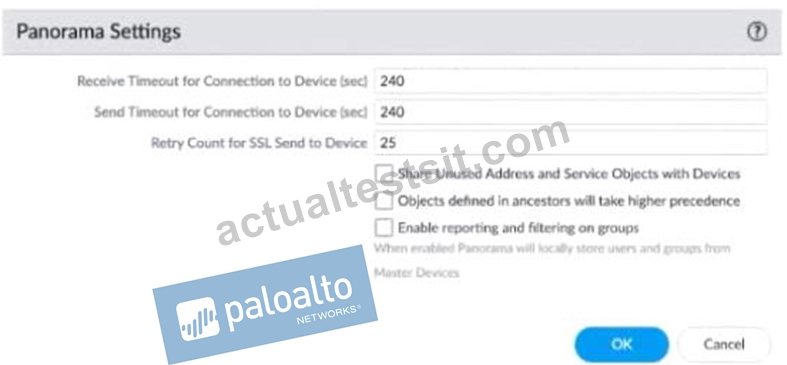
An administrator cannot see any Traffic logs from the Palo Alto Networks NGFW in Panorama reports. The configuration problem seems to be on the firewall Which settings, if configured incorrectly, most likely would stop only Traffic logs from being sent from the NGFW to Panorama?
A)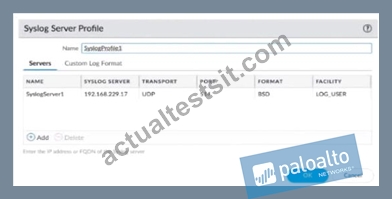
B)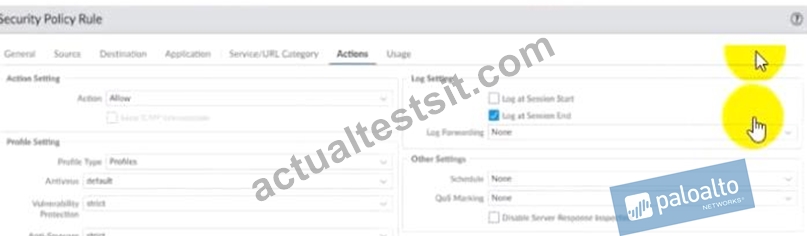
C)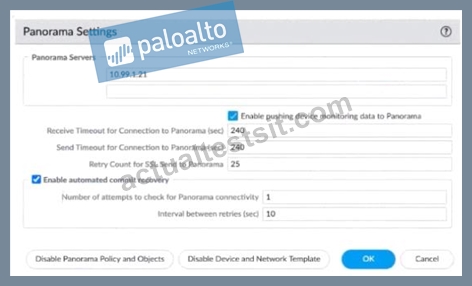
- A. Option A
- B. Option D
- C. Option B
- D. Option C
Answer: C
NEW QUESTION # 68
To connect the Palo Alto Networks firewall to AutoFocus, which setting must be enabled?
- A. Device> Setup>Management >AutoFocus
- B. Device>Setup>Services>AutoFocus
- C. Device>Setup>WildFire>AutoFocus
- D. Device>Setup> Management> Logging and Reporting Settings
- E. AutoFocus is enabled by default on the Palo Alto Networks NGFW
Answer: A
Explanation:
Reference:
https://www.paloaltonetworks.com/documentation/71/pan-os/pan-os/getting-started/enable-autofocus-threat-inte
NEW QUESTION # 69
What are three reasons for excluding a site from SSL decryption? (Choose three.)
- A. unsupported ciphers
- B. unsupported browser version
- C. the website is not present in English
- D. certificate pinning
- E. mutual authentication
Answer: A,D,E
Explanation:
Explanation
Reasons that sites break decryption technically include pinned certificates, client authentication, incomplete certificate chains, and unsupported ciphers.https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-admin/decryption/decryption-exclusions/exclude-
NEW QUESTION # 70
Several offices are connected with VPNs using static IPV4 routes. An administrator has been tasked with implementing OSPF to replace static routing.
Which step is required to accoumplish this goal?
- A. Create new VPN zones at each site to terminate each VPN connection
- B. Assign an IP address on each tunnel interface at each site
- C. Assign OSPF Area ID 0.0.0.0 to all Ethernet and tunnel interfaces
- D. Enable OSPFv3 on each tunnel interface and use Area ID 0.0.0.0
Answer: C
NEW QUESTION # 71
A network administrator troubleshoots a VPN issue and suspects an IKE Crypto mismatch between peers.
Where can the administrator find the corresponding logs after running a test command to initiate the VPN?
- A. Traffic logs
- B. Tunnel Inspection logs
- C. Configuration logs
- D. System logs
Answer: D
Explanation:
Explanation
According to the Palo Alto Networks documentation, "To view IKE and IPSec Crypto profiles in the logs, filter the System log for eventid equal to vpn (Monitor > Logs > System)." References:https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/vpn/set-up-site-to-site-vpn/set-up-ike-c
NEW QUESTION # 72
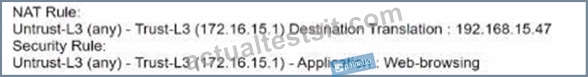
A user at an external system with the IP address 65.124.57.5 queries the DNS server at 4. 2.2.2 for the IP address of the web server, www,xyz.com. The DNS server returns an address of 172.16.15.1 In order to reach Ire web server, which Security rule and NAT rule must be configured on the firewall?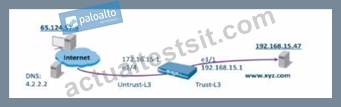
- A.
- B.
- C.
- D.
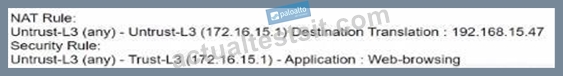
Answer: D
Explanation:
Explanation
The addresses used in destination NAT rules always refer to the original IP address in the packet (that is, the pre-translated address). The destination zone in the NAT rule is determined after the route lookup of the destination IP address in the original packet (that is, the pre-NAT destination IP address). The addresses in the security policy also refer to the IP address in the original packet (that is, the pre-NAT address). However, the destination zone is the zone where the end host is physically connected. In other words, the destination zone in the security rule is determined after the route lookup of the post-NAT destination IP address.
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/networking/nat/nat-configuration-examples/destinat
NEW QUESTION # 73
What can missing SSL packets when performing a packet capture on dataplane interfaces?
- A. There is a hardware problem with offloading FPGA on the management plane
- B. The missing packets are offloaded to the management plane CPU
- C. The packets are not captured because they are encrypted
- D. The packets are hardware offloaded to the offloaded processor on the dataplane
Answer: D
NEW QUESTION # 74
A network engineer is troubleshooting a VPN and wants to verify whether the decapsulation/encapsulation counters are increasing. Which CLI command should the engineer run?
- A. Show vpn ipsec-sa tunnel <tunnel name>
- B. Show vpn tunnel name | match encap
- C. Show vpn flow name <tunnel name>
- D. Show running tunnel flow lookup
Answer: C
NEW QUESTION # 75
Refer to the exhibit.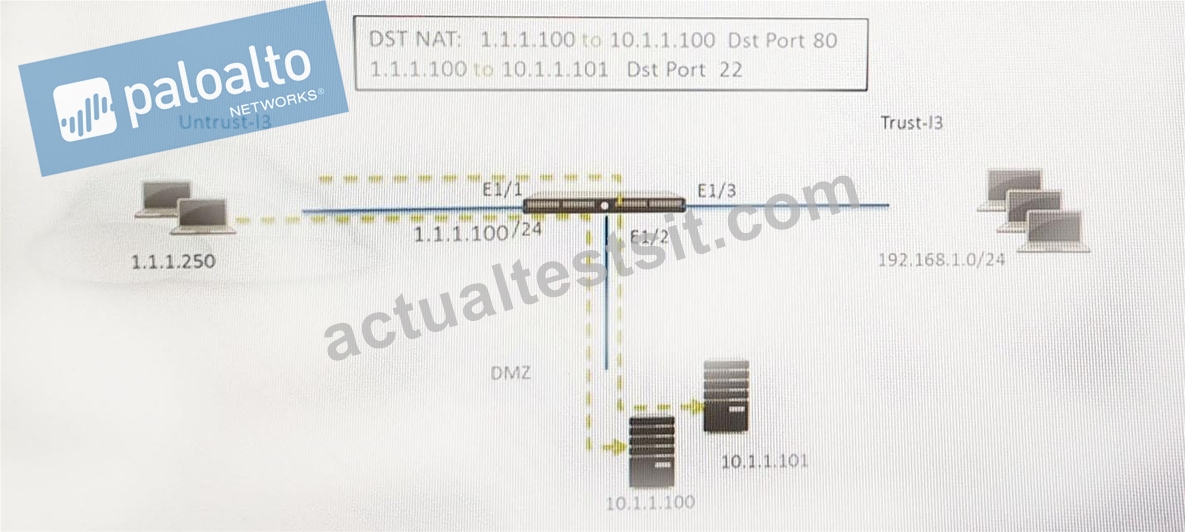
An administrator is using DNAT to map two servers to a single public IP address. Traffic will be steered to the specific server based on the application, where Host A (10.1.1.100) receives HTTP traffic and HOST B (10.1.1.101) receives SSH traffic.) Which two security policy rules will accomplish this configuration? (Choose two.)
- A. Untrust (Any) to DMZ (10.1.1.1), ssh -Allow
- B. Untrust (Any) to Untrust (10.1.1.1), ssh -Allow
- C. Untrust (Any) to Untrust (10.1.1.1), web-browsing -Allow
- D. Untrust (Any) to DMZ (10.1.1.100.10.1.1.101), ssh, web-browsing -Allow
- E. Untrust (Any) to DMZ (10.1.1.1), web-browsing -Allow
Answer: A,E
Explanation:
Explanation
https://docs.paloaltonetworks.com/pan-os/8-0/pan-os-admin/networking/nat/nat-configuration-examples/destinat
NEW QUESTION # 76
Which two methods can be used to verify firewall connectivity to AutoFocus? (Choose two.)
- A. Verify AutoFocus is enabled below Device Management tab.
- B. Check for WildFire forwarding logs.
- C. Verify AutoFocus status using CLI.
- D. Check the license
- E. Check the WebUI Dashboard AutoFocus widget.
Answer: A,D
Explanation:
Explanation/Reference:
Reference: https://www.paloaltonetworks.com/documentation/80/pan-os/pan-os/getting-started/enable- autofocus-threat-intelligence
NEW QUESTION # 77
An administrator notices that an interlace configuration has been overridden locally on a firewall. They require an configuration to be managed from Panorama and overrides are not allowed. What is one way the administrator can meet this requirement?
- A. Reload the running configuration and perform a Firewall local commit.
- B. Perform a device-group commit push from Panorama using the "Include Device and Network Templates" option.
- C. Perform a commit force from the CLI of the firewall.
- D. Perform a template commit push from Panorama using the "Force Template Values'' option
Answer: D
NEW QUESTION # 78
A bootstrap USB flash drive has been prepared using a Windows workstation to load the initial configuration of a Palo Alto Networks firewall that was previously being used in a lab. The USB flash drive was formatted using file system FAT32 and the initial configuration is stored in a file named init-cfg txt. The firewall is currently running PAN-OS 10.0 and using a lab config The contents of init-cfg txi in the USB flash drive are as follows: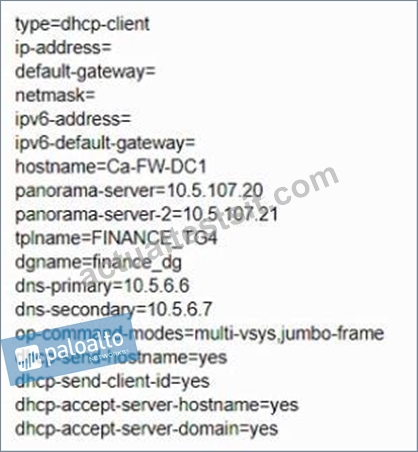
The USB flash drive has been inserted in the firewalls' USB port, and the firewall has been restarted using command:> request resort system Upon restart, the firewall fails to begin the bootstrapping process. The failure is caused because
- A. The bootstrap.xml file is a required file but it is missing
- B. The USB must be formatted using the ext3 file system, FAT32 is not supported
- C. Firewall must be in factory default state or have all private data deleted for bootstrapping
- D. PANOS version must be 91.x at a minimum but the firewall is running 10.0.x
- E. The hostname is a required parameter, but it is missing in init-cfg txt
Answer: B
Explanation:
https://docs.paloaltonetworks.com/pan-os/8-1/pan-os-admin/firewall-administration/bootstrap-the-firewall/bootstrap-a-firewall-using-a-usb-flash-drive.html#id8378007f-d6e5-4f2d-84a4-5d50b0b3ad7d
NEW QUESTION # 79
To support a new compliance requirement, your company requires positive username attribution of every IP address used by wireless devices You must collect IP address-to-username mappings as soon as possible with minimal downtime and minimal configuration changes to the wireless devices themselves The wireless devices are from various manufacturers
Given the scenario, choose the option for sending IP address-to-username mappings to the firewall
- A. XFF headers
- B. syslog listener
- C. RADIUS
- D. UID redistribution
Answer: B
NEW QUESTION # 80
......
Get The Important Preparation Guide With PCNSE Dumps: https://protechtraining.actualtestsit.com/Palo-Alto-Networks/PCNSE-exam-prep-dumps.html